Frequently asked questions about reported Citrix NetScaler zero-day vulnerabilities

CVE-2026-88771 and CVE-2026-88772, two zero-day vulnerabilities in Citrix NetScaler, have been confirmed as exploited in the wild. Citrix released patches on September 27, 2026.
Change log
Update September 27: Citrix published security bulletin CTX697096, confirming CVE-2026-88771 and CVE-2026-88772 as the two zero-day RCE vulnerabilities and releasing patches. Post updated with CVE IDs, CVSS scores, patch versions, and IoC guidance.
Click here to review the change log history
Update September 27: Citrix published security bulletin CTX697096, confirming CVE-2026-88771 and CVE-2026-88772 as the two zero-day RCE vulnerabilities and releasing patches. Post updated with CVE IDs, CVSS scores, patch versions, and IoC guidance.
September 27: Original publication based on limited public information ahead of Citrix's official advisory.
Key takeaways
- Citrix has confirmed two critical zero-day vulnerabilities in NetScaler ADC and NetScaler Gateway, both capable of remote code execution and actively exploited in the wild.
- Citrix released patches on September 27, 2026.
- Citrix says generic indicators of compromise will be available through NetScaler Console, and customers can request them from Citrix Support.
Background
Tenable's Research Special Operations (RSO) team has compiled this blog to answer Frequently Asked Questions (FAQ) regarding two reported zero-day vulnerabilities in Citrix NetScaler that sources say were actively exploited in the wild. The following FAQ is based on limited public information. This post was last updated on September 27, 2026 following publication of the official Citrix security bulletin.
FAQ
What is the source of the NetScaler vulnerabilities?
On September 25, 2026, reports surfaced through a reddit post on r/Citrix regarding advice to shut down “Netscalers.” This included a report from a user that said this information came from the “Dutch national cyber security center” and further details included a note about two zero-day vulnerabilities.
On September 26, 2026, additional reports confirming the existence of these flaws became public, including social posts from researchers at watchTowr on X, as well as Kevin Beaumont on Mastodon.
What is the context surrounding the Dutch National Cyber Security Centre (NCSC-NL) alert?
The Reddit post on r/Citrix cited details from an NCSC-NL pre-notification that had not yet been made public. Community members in that thread said the pre-notification was distributed under Traffic Light Protocol (TLP):AMBER+STRICT restrictions. Tenable's RSO has not independently obtained or reviewed the contents of this notification.
Has Citrix confirmed the presence of zero-day vulnerabilities?
Yes. Citrix published a security bulletin (CTX697096) on September 27, 2026, confirming two zero-day vulnerabilities and noting that both CVEs have been observed being exploited against customer deployments.
What are these zero-day vulnerabilities?
Citrix has confirmed two zero-day vulnerabilities in NetScaler ADC and NetScaler Gateway. CVE-2026-88771 affects all deployments, including default configurations. CVE-2026-88772 requires Datagram Transport Layer Security (DTLS) to be enabled, which is the default on VPN virtual servers.
| CVE | Description | CVSSv4 |
|---|---|---|
| CVE-2026-88771 | Citrix NetScaler ADC and NetScaler Gateway Improper Input Validation vulnerability | 9.5 |
| CVE-2026-88772 | Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability | 9.5 |
Citrix also addressed six additional vulnerabilities affecting various configurations:
| CVE | Description | CVSSv4 |
|---|---|---|
| CVE-2026-88773 | Citrix NetScaler ADC and NetScaler Gateway HTTP Request Smuggling vulnerability | 9.3 |
| CVE-2026-88774 | Citrix NetScaler ADC and NetScaler Gateway Feature Policy Bypass vulnerability | 7.0 |
| CVE-2026-88775 | Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability | 8.8 |
| CVE-2026-88776 | Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability | 8.8 |
| CVE-2026-88777 | Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability | 8.8 |
| CVE-2026-88778 | Citrix NetScaler ADC and NetScaler Gateway TCP ISN Prediction vulnerability | 8.8 |
watchTowr originally confirmed details for the zero-days on September 26, 2026:
We have been made aware of further info, which we are sharing. We had no idea Citrix sysadmins were like GTA6 fans - so friendly 🤗
Please, direct further questions to Citrix. We are not Citrix PSIRT (despite it occasionally looking that way).
Citrix comms & patches are… https://t.co/OemTXwG8PB— watchTowr (@watchtowrcyber) September 26, 2026
Are these zero-day vulnerabilities related to CVE-2026-19490 and CVE-2026-19489?
No. Neither CVE-2026-19490 nor CVE-2026-19489 appears to be related. Both are previously disclosed vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway for which patches are available. CVE-2026-19490 was added to CISA's Known Exploited Vulnerabilities (KEV) catalog on September 9, 2026.
Reports say these vulnerabilities were exploited. How widespread are the attacks?
Based on public reporting, it has not been determined whether exploitation has reached widespread scale. On September 26, Kevin Beaumont stated: “The Netscaler zero day thing is real, being used in active attacks. No patch yet, if sensitive to Netscaler vulns switch it off.”
How many Citrix NetScaler vulnerabilities have been exploited in the wild in the past?
Citrix NetScaler devices have historically been a popular target for attackers. Including CVE-2026-19490, as of September 27, 2026, there were 13 NetScaler-related entries in CISA's KEV catalog and 24 entries for Citrix products overall. The RSO team has covered several notable incidents:
| CVE | Description | KEV added | Ransomware | Tenable blogs |
|---|---|---|---|---|
| CVE-2026-8452 | Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability | 2026-08-26 | Unknown | - |
| CVE-2026-3055 | Citrix NetScaler Out-of-Bounds Read vulnerability | 2026-03-30 | Unknown | - |
| CVE-2025-7775 | Citrix NetScaler Memory Overflow vulnerability | 2025-08-26 | Unknown | CVE-2025-7775: Citrix NetScaler ADC and NetScaler Gateway Zero-Day Remote Code Execution Vulnerability Exploited in the Wild |
| CVE-2025-5777 | Citrix NetScaler ADC and Gateway Out-of-Bounds Read vulnerability (“CitrixBleed 2”) | 2025-07-10 | Known | CVE-2025-5777, CVE-2025-6543: Frequently Asked Questions About CitrixBleed 2 and Citrix NetScaler Exploitation |
| CVE-2025-6543 | Citrix NetScaler ADC and Gateway Buffer Overflow vulnerability | 2025-06-30 | Unknown | CVE-2025-5777, CVE-2025-6543: Frequently Asked Questions About CitrixBleed 2 and Citrix NetScaler Exploitation |
| CVE-2023-6549 | Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability | 2024-01-17 | Unknown | CVE-2023-6548, CVE-2023-6549: Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC and NetScaler Gateway |
| CVE-2023-6548 | Citrix NetScaler ADC and NetScaler Gateway Code Injection vulnerability | 2024-01-17 | Unknown | CVE-2023-6548, CVE-2023-6549: Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC and NetScaler Gateway |
| CVE-2023-4966 | Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability (“CitrixBleed”) | 2023-10-18 | Known | [1] [2] [3] |
| CVE-2023-3519 | Citrix NetScaler ADC and NetScaler Gateway Code Injection vulnerability | 2023-07-19 | Known | CVE-2023-3519: Critical RCE in Netscaler ADC (Citrix ADC) and Netscaler Gateway (Citrix Gateway) |
| CVE-2020-8193 | Citrix ADC, Gateway, and SD-WAN WANOP Appliance Authorization Bypass vulnerability | 2021-11-03 | Unknown | Government Agencies Warn of State-Sponsored Actors Exploiting Publicly Known Vulnerabilities |
| CVE-2019-19781 | Citrix ADC, Gateway, and SD-WAN WANOP Appliance Code Execution vulnerability | 2021-11-03 | Known | [1] [2] |
Which threat actors are exploiting these vulnerabilities?
No details about threat actors have been made public at this time. However, based on our research, roughly two-thirds of threat actor activity targeting Citrix NetScaler over the last seven years involved advanced persistent threat (APT) groups, while one-third involved ransomware groups and their affiliates.
Is there a proof-of-concept (PoC) available for these vulnerabilities?
As of September 27, 2026, there are no public proofs-of-concept (PoCs) for CVE-2026-88771 or CVE-2026-88772.
Are patches or mitigations available?
Yes. Citrix urges customers running affected versions to install one of the updated versions.
| Product Branch | Affected Versions | Fixed Versions |
|---|---|---|
| NetScaler ADC and NetScaler Gateway 14.1 | Before 14.1-73.37 | 14.1-73.37 and later |
| NetScaler ADC and NetScaler Gateway 13.1 | Before 13.1-64.23 | 13.1-64.23 and later |
| NetScaler ADC 14.1-FIPS | Before 14.1-73.37 FIPS | 14.1-73.37 FIPS and later |
| NetScaler ADC 13.1-FIPS and 13.1-NDcPP | Before 13.1-37.279 | 13.1-37.279 and later |
Citrix's bulletin lists fixes only for the 14.1 and 13.1 branches. NetScaler ADC and NetScaler Gateway versions 12.1 and 13.0 have reached end-of-life (EOL) and no longer receive security updates, and Citrix has not said whether they are affected by these vulnerabilities.
Are there any indicators of compromise for these vulnerabilities?
Citrix says it will provide generic indicators of compromise (IoCs) through NetScaler Console (version 14.1-73.36 or later, with telemetry enabled) once the feature is released. Customers who do not use NetScaler Console, or cannot access the feature, can contact Citrix Support to request the IoCs. Citrix notes that the IoC information may not cover all threat actor tactics, techniques and procedures (TTPs) and recommends engaging forensic investigators for a comprehensive assessment.
Has Tenable Research classified these vulnerabilities as part of Vulnerability Watch?
Yes. Both CVE-2026-88771 and CVE-2026-88772 have been classified as "Vulnerability of Interest" as part of Vulnerability Watch.
Has Tenable released any product coverage for these vulnerabilities?
A list of Tenable plugins for these vulnerabilities can be found on the individual CVE pages for CVE-2026-88771 and CVE-2026-88772 as they’re released. This link will display all available plugins for these vulnerabilities, including upcoming plugins in our Plugins Pipeline.
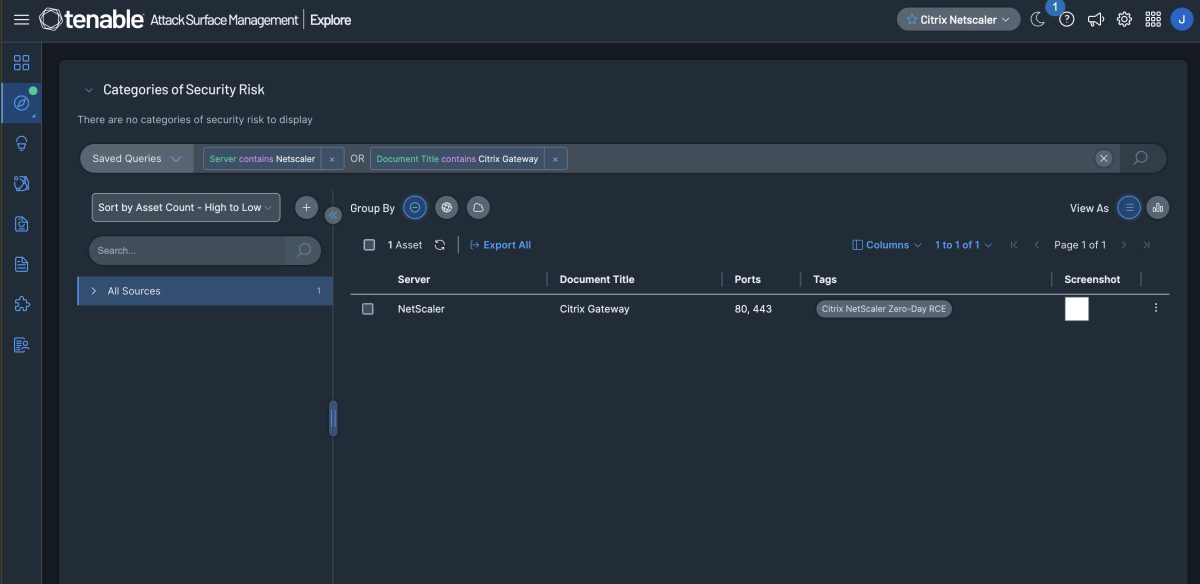
Additionally, customers can utilize Tenable Attack Surface Management to identify public-facing NetScaler assets by using the following query: Server Contains Netscaler OR Document Title contains Citrix Gateway
Get more information
- Citrix Security Bulletin CTX697096: NetScaler ADC and NetScaler Gateway Security Bulletin
- Citrix Community: NetScaler ADC and NetScaler Gateway Security Bulletin (CVE-2026-88771 through CVE-2026-88778)
- Reddit r/Citrix thread: “Netscaler leak?”
- watchTowr post on X: Citrix NetScaler RCE confirmation
- Kevin Beaumont on Mastodon: Zero-day confirmation
Join Tenable's Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.
Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
Learn more
Learn more
Related articles


- Exposure Management
- Vulnerability Management
Tenable One
Request a demo
The world’s leading AI-powered exposure management platform.
Thank You
Thank you for your interest in Tenable One.
A representative will be in touch soon.
Form ID: 7469
Form Name: one-eval
Form Class: c-form form-panel__global-form c-form--mkto js-mkto-no-css js-form-hanging-label c-form--hide-comments
Form Wrapper ID: one-eval-form-wrapper
Confirmation Class: one-eval-confirmform-modal
Simulate Success